Park24 confirms unauthorized access to Times Car web system
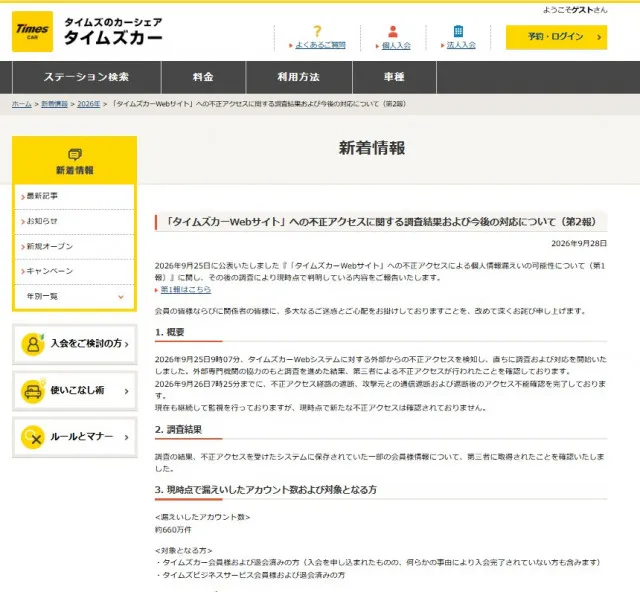
Park24, the operator of Japan’s Times Car car-sharing service, has announced that information connected to approximately 6.6 million accounts was obtained through unauthorized access to the company’s Times Car web system. The announcement was published on the company’s official website on the 28th.
The affected records include current members, people who had already cancelled their memberships and individuals who applied to join but did not complete the enrollment process. Park24 said the information exposed varies by person and may include names, department names for corporate members, addresses, dates of birth, telephone numbers, email addresses, driver’s license information, images of identification documents such as driver’s licenses, passwords and IDs linked to external services.
The company stated that credit card information was not affected.
Attack detected and access blocked
According to Park24, the company detected external unauthorized access to the Times Car web system at 9:07 a.m. on the 25th. It immediately began investigating the incident and taking countermeasures, with support from outside cybersecurity specialists. The investigation confirmed that a third party had accessed the system without authorization and had obtained some member information stored there.
By 7:25 a.m. on the 26th, Park24 said it had blocked the route used for the unauthorized access, cut off communication with the apparent source of the attack and confirmed that the system could no longer be accessed through that route. The company continues to monitor the system and said that no new unauthorized access has been confirmed at this stage.
What Times Car users should do
Park24 is urging current and former users, as well as applicants, to be particularly cautious of emails, text messages and phone calls pretending to come from the company. People should not open unfamiliar links or attachments, or enter passwords, authentication codes or credit card details in response to unexpected messages.
The company emphasized that it will not ask customers for passwords or credit card information by email, SMS or telephone. Users who receive suspicious communications should avoid responding directly and should verify information through the official Times Car website or customer support channels.
Why the incident matters in Japan
Car sharing has become a practical transportation option in Japan, particularly in urban areas where parking can be expensive and many residents do not own a vehicle. Times Car allows registered users to reserve vehicles through digital services and access cars at designated locations, making the protection of account and identity information essential to everyday mobility.
The incident also highlights the wider risks faced by digital services that hold information from large numbers of users over many years. Because the reported records include former members and incomplete applicants, people who no longer use Times Car may also need to remain alert for targeted phishing attempts. Park24’s investigation and monitoring are continuing, and the company may provide further updates as more details become available.
For users in Japan and foreign residents who rely on car-sharing services, the case is a reminder to use unique passwords, enable additional security measures where available and treat unexpected requests for personal information with caution.