Cyberattack causes disruption across Japan
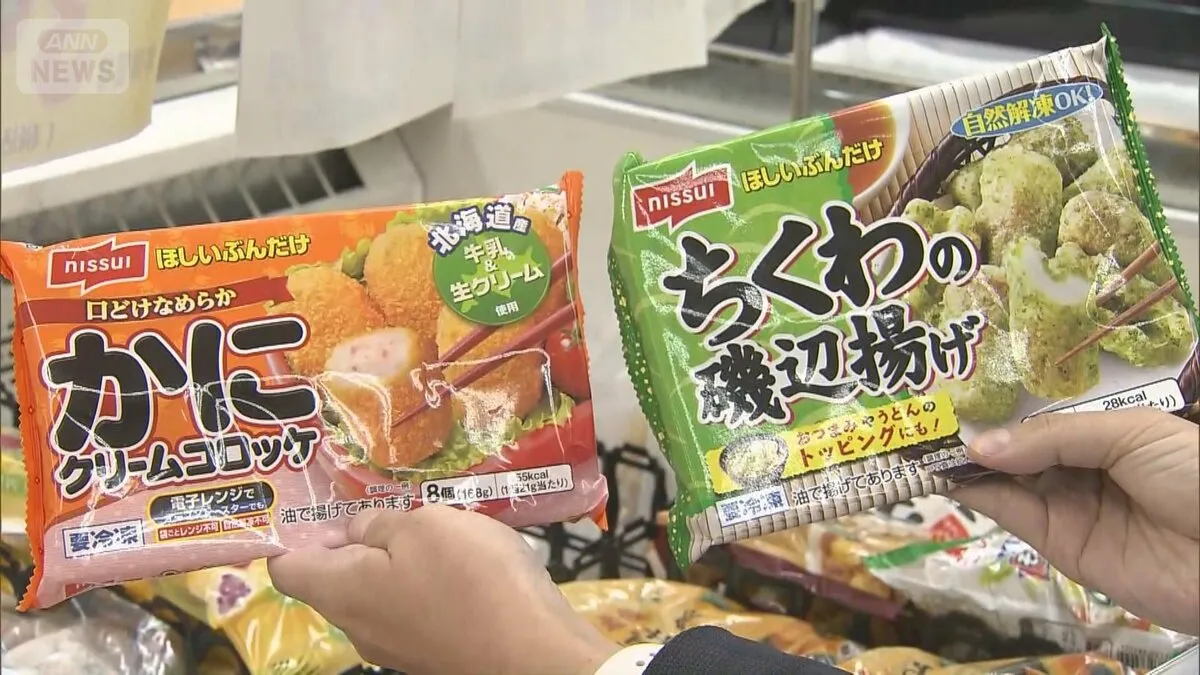
A cyberattack on part of a data center used by Nissui Logistics, a group company of major Japanese food producer Nissui, has disrupted systems and halted the movement of goods. The incident highlights the growing vulnerability of Japan’s increasingly digital economy, where a single technology provider can support services used by hundreds of companies, local governments and public organizations.
Nissui said that the unauthorized access affected servers at a data center operated by IDC Frontier, a SoftBank subsidiary. As a result, Nissui Logistics has been unable to receive or ship products normally. The company is investigating whether personal information or other data managed by the group was taken outside the system.
Retailers face immediate supply concerns
The disruption has created uncertainty for supermarkets and other businesses that depend on reliable deliveries. A food buyer at Super Cellcio Wadamachi store in Yokohama said the store had only about two days’ worth of inventory for some products. If manufacturers cannot release goods, retailers may need to arrange emergency supplies quickly, potentially affecting shelves and customers.
IDC Frontier said that part of its server infrastructure in Shirakawa, Fukushima Prefecture, was attacked at around 3:40 a.m. on the seventh. The incident involved ransomware, a form of malware that encrypts data and demands payment from victims. The company said the affected cloud service had no clear recovery timetable while its investigation continued, describing the situation as serious.
Impact extends to public websites
The cloud platform is used by 495 organizations, including Nissui Logistics, childcare service providers and government-related websites. Ibaraki Prefecture reported that officials were told servers had shut down, leaving prefectural and police websites temporarily inaccessible. The incident demonstrates why cloud security is now a national concern: an attack on one provider can create simultaneous problems for businesses, municipalities and residents.
Japan’s government convened a meeting involving relevant ministries and agencies and decided to centralize information through the National Cybersecurity Office. Discussions included the need for organizations to manage data appropriately and delete information that is no longer necessary. Such measures are particularly important in Japan, where local governments, healthcare providers, manufacturers and retailers are rapidly expanding online services.
AI lowers the barrier for attackers
Cybersecurity specialists say artificial intelligence is adding a new dimension to the threat. In a demonstration conducted with a Japanese cybersecurity company, an AI-based tool scanned a fictional online shopping website, searched for weaknesses and identified personal information in roughly 10 minutes. Experts emphasized that AI does not necessarily create entirely new hacking techniques; rather, it can carry out familiar tasks far more quickly and allow people with limited technical knowledge to launch attacks.
Researchers have also reported cases in which publicly available AI systems performed cyber-related tasks with limited instructions. Stolen names, telephone numbers and online account credentials can be sold on illegal marketplaces. One reported listing offered billions of account records, underscoring the global scale of the data-trading problem, although the authenticity and origin of such listings can be difficult to verify.
Japan and the international warning
The concern is not limited to Japan. Authorities and companies in the United States, Denmark and South Korea have also reported major data-security incidents or suspected AI-assisted attacks. In Denmark, government officials warned people not to disclose card details or passwords even if contacted by someone who knows their identification number. In South Korea, officials said AI may have been involved in an incident affecting personal information held by financial institutions.
Japanese cybersecurity experts warn that future attacks could target critical infrastructure, including electricity, transportation and traffic-control systems. They say perfect prevention remains difficult because attackers can repeatedly probe many potential weaknesses, while defenders must prevent every successful intrusion. The most practical response, they argue, is preparation: maintain offline backups, limit stored personal data, monitor networks continuously, rehearse emergency response plans and restore services quickly after an attack.
For companies and public bodies in Japan, the incident is a reminder that digital convenience must be matched by strong resilience. For residents and foreign businesses operating in Japan, basic precautions remain essential, including using unique passwords, enabling multifactor authentication and treating unexpected requests for personal information with caution.