JR Kyushu reports potential data exposure
JR Kyushu, the railway operator serving Japan’s southern Kyushu region, announced on the 9th that the email addresses of up to approximately 1.3 million users registered with its web-based membership service may have been leaked. The company said that no personal information other than email addresses has been identified as exposed at this stage.
The incident was linked to unauthorized access involving a corporate cloud service provided by IDC Frontier, a Tokyo-based information technology company and subsidiary of SoftBank. JR Kyushu uses the service to support certain online operations, including the distribution of email newsletters. Following the incident, the company said it became unable to send its newsletters.
Customers to receive individual notifications
JR Kyushu said it plans to send apology and notification emails to customers whose information may have been affected once preparations are complete. The company has not indicated that other categories of customer data, such as names, addresses, telephone numbers, payment details or travel records, were involved in the reported exposure.
For affected customers, the most immediate concern is the possible misuse of their email addresses. Email addresses can be used in phishing campaigns, in which criminals impersonate trusted companies to encourage recipients to click malicious links, reveal passwords or provide financial information. Customers should therefore be cautious about unexpected messages claiming to be from JR Kyushu or other transport and travel-related services. Checking the sender’s address carefully and accessing official websites directly, rather than through links in emails, are sensible precautions.
Why the incident matters in Japan
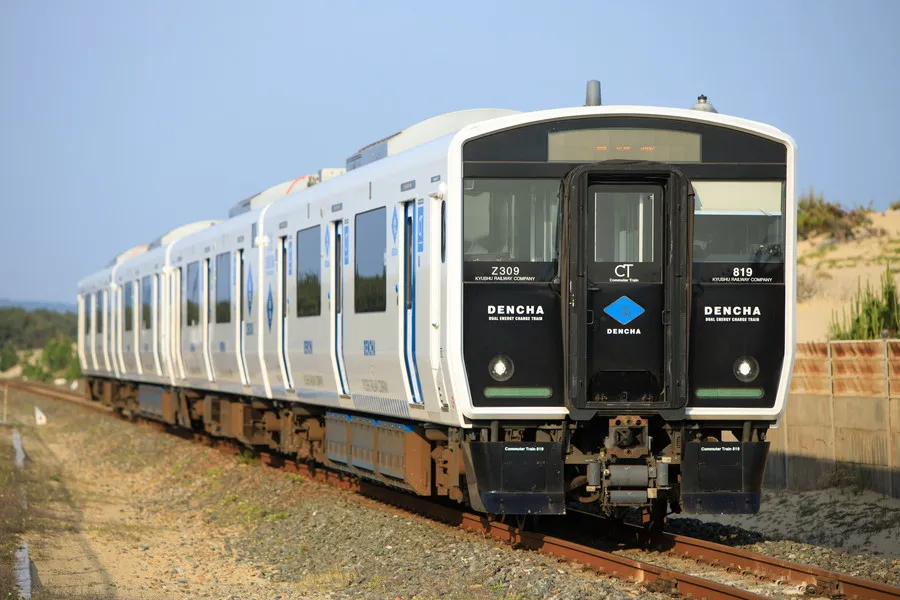
JR Kyushu operates an important rail network across Kyushu, including services connecting major cities such as Fukuoka, Kumamoto, Kagoshima and Nagasaki. The company also provides online services for customers, making its digital membership systems relevant to both residents and international visitors who use Japan’s railways for travel, reservations and tourism information.
The case also highlights the growing importance of cybersecurity in Japan’s transport and infrastructure sectors. Rail companies increasingly rely on cloud platforms and external technology providers for communications, customer services and business operations. These systems can improve efficiency and convenience, but an incident involving a third-party provider can also affect large numbers of users at once.
Further information expected
JR Kyushu’s announcement did not state that the information had definitely been taken in every case, describing the exposure as a possibility. The company is expected to provide further guidance directly to potentially affected customers as its review progresses. Until then, customers should monitor their inboxes, remain alert to suspicious communications and avoid sharing passwords or payment information in response to unsolicited messages.
The incident serves as a reminder that even limited data, such as an email address, can have security implications when held in large databases. JR Kyushu’s planned notifications will be important in helping customers understand whether their information was included and what steps, if any, they should take.